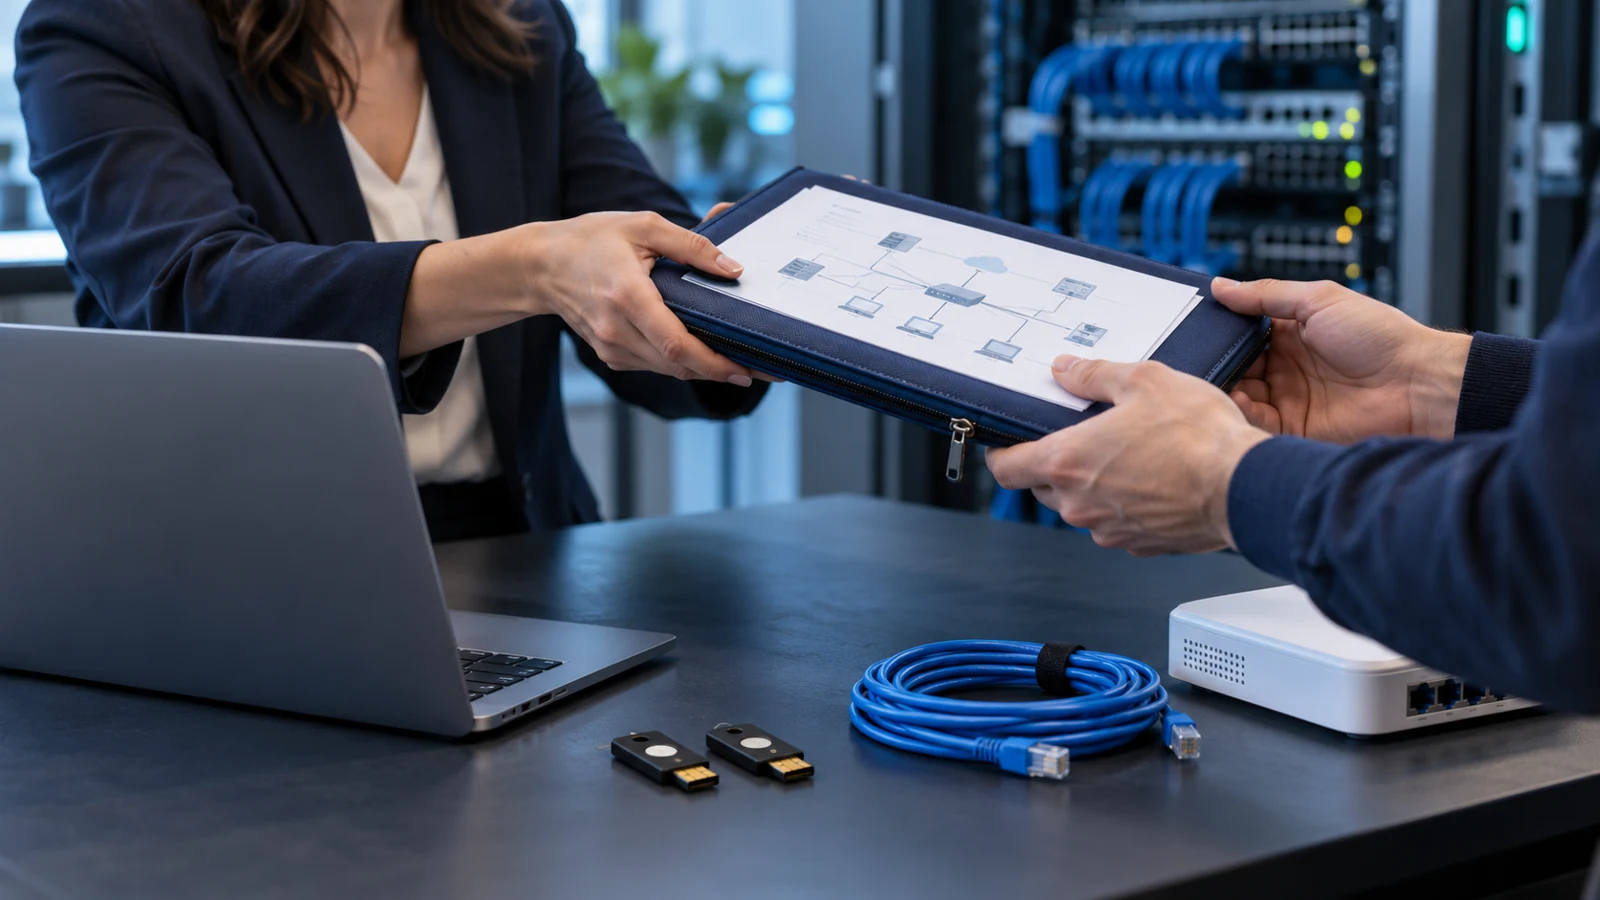
Before signing off an IT provider change, ask for a handover pack that identifies your systems, confirms who controls them and records what the incoming provider has tested. Treat this as a practical acceptance check. A folder of passwords is not enough to show that someone can support the business on Monday morning.
Agree the pack and its acceptance criteria before the outgoing service ends. The NCSC recommends defining supplier and customer responsibilities clearly in the contract.[1] For the handover itself, ask both providers to name the person completing each action, the person checking it and any unresolved dependency. Keep a business owner involved in approving the result.
Build a record someone else can use
Request a current inventory covering computers, servers, network equipment and business applications. For each service, record its purpose, account owner, renewal contact and support route. Include your domain registrar, website hosting and telephone supplier rather than limiting the document to equipment in the office. Mark entries that still need confirmation.
Ask the incoming engineer to use the documentation during the handover meeting. Can they identify which connection serves reception, where shared files live and who supports your accounting software? Record corrections while both suppliers are available. Keep diagrams readable and store the final version somewhere your authorised business contact can retrieve independently.
Verify access without circulating passwords
Ask for a supervised check of business-controlled administration and recovery arrangements. Identify who approves access, where credentials are held and how authorised staff recover access if their normal contact is unavailable. Use an agreed secure transfer method. Do not paste passwords into the handover spreadsheet or send them around a group email.
Have the incoming provider document the permissions it needs. The NCSC recommends least privilege and two-step verification for supplier access.[1] Request evidence that the agreed accounts work and their authentication methods are ready. Keep sensitive recovery material separate from the general equipment record, with a named owner responsible for its custody.
Check Microsoft partner access separately
Include a review of Microsoft 365 partner relationships, not just the users listed in your directory. Microsoft documents delegated administration through GDAP as granular, time-bound partner access.[2] Ask your incoming provider to explain the roles it requests and record who authorises them. Keep subscription billing and technical access as separate handover questions.
Microsoft says a customer can remove a partner’s delegated administration while retaining the relationship for subscription and licence renewals.[3] Ask the administrator to review the actual arrangement before changing anything. If you use Azure, include its role assignments too: Microsoft warns that removing delegated administration does not remove separately assigned Azure subscription permissions.[3]
Ask for recovery evidence and outstanding work
Request the backup service details, protected systems and recovery contacts. Ask for the date, scope and result of the latest restore test. The NCSC advises checking backup arrangements and how often recovery is tested.[1] For this handover, agree a safe demonstration using non-sensitive test material rather than restoring over live business files.
Give the incoming provider an open-work register. Include unresolved faults, expiring equipment support and changes already promised to staff. Ask it to distinguish something accepted for investigation from something fixed and checked. Assign dates for reviewing each outstanding item so the handover does not quietly close work nobody has completed.
Set an order for removing old access
Ask both providers to agree when support responsibility changes and which access must remain temporarily for agreed tasks. Have the incoming engineer identify remote support tools, administrator accounts and other supplier connections that need review. Avoid blanket deletion during the meeting. Require an owner, approval and a recovery plan for each proposed change.
Once the new arrangements have been checked, ask for confirmation that obsolete access has been removed. The NCSC says access should end when the job is completed.[1] Record any temporary exception with its purpose and review date. Request a final access record for your business files, rather than accepting a general assurance that everything has been tidied up.
Sign off against ordinary working tasks
Choose a few tasks your staff actually rely on and have them demonstrate those tasks after the change. Include a support request through the new contact route. Record the result, any remaining problem and who owns it. Agree what would stop sign-off and what can remain on a dated follow-up register.
BMT’s broader switching guide covers selecting a supplier and planning the transition.[4] This acceptance check addresses the technical evidence to request at its end. Bring your current service list and unresolved questions to a handover discussion with BMT, so the next step is a defined review rather than an assumption that everything transferred.
Sources
[1] NCSC: choosing a managed service provider
[2] Microsoft: GDAP frequently asked questions